Morocco Unveils Bill to Digitize Judicial Procedures

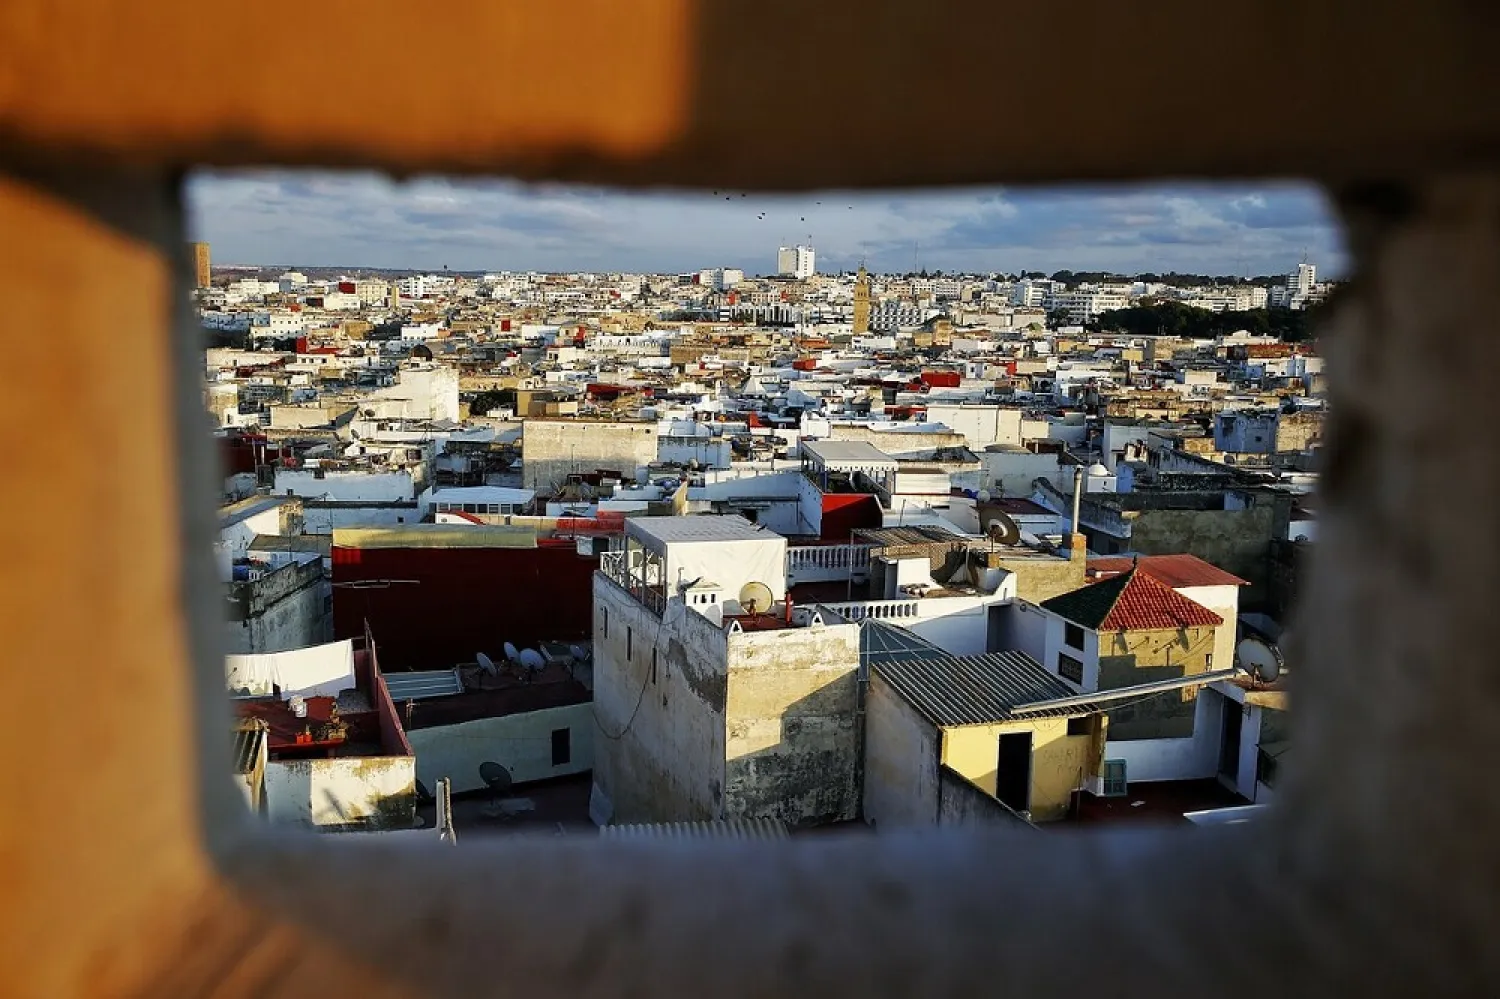
Rooftops of Rabat's Medina are seen from atop a hotel that is being reconstructed September 25, 2014. (Reuters)
TT

Morocco Unveils Bill to Digitize Judicial Procedures

Rooftops of Rabat's Medina are seen from atop a hotel that is being reconstructed September 25, 2014. (Reuters)

Moroccan Justice Minister Abdellatif Ouahbi said his ministry has prepared a draft law to regulate the digitization of judicial procedures in the civil and criminal fields.

His remarks were made on Monday during an international seminar held in Tangier on the “legislative basis for the digitization of judicial procedures.”

The bill aims at facilitating using digital systems in civil litigation procedures to submit articles of claims, requests, appeals and all judicial procedures electronically before Morocco’s various courts.

According to Ouahbi, it calls for adopting the e-payment system to pay for a judicial fee or a financial procedure, approving professional e-accounts for lawyers, judicial commissioners and experts to help communicate with the courts, as well as approving e-signatures and e-addresses for public administrations and other legal persons and determining the legal impact of the procedures.

The minister explained that the draft law targets using digitization in all stages of the lawsuits, while providing the same guarantees granted to the parties during trials with physical presence and in the same order of effect.

Under the bill, relevant parties may carry out research and investigation, hold virtual hearings and trials remotely through the visual debate technology with the consent of the accused.

The bill further ensures the informational processing of the minutes completed in line with the civil and criminal lawsuit procedures and their e-signature by the party authorized by the law to do so, in addition to the informational processing of the criminal record cards and their e-signature.

The seminar was organized by the ministry “to keep pace with the reform workshops organized by the Moroccan government” to implement the “Digital Transformation of Administration” project by boosting cooperation and exchanging experiences and best practices among various countries in this field.


Eight US States Sue OpenAI, Claiming ChatGPT Harms Young Users

A keyboard is placed in front of a displayed OpenAI logo in this illustration taken February 21, 2023. (Reuters)
TT

Eight US States Sue OpenAI, Claiming ChatGPT Harms Young Users

A keyboard is placed in front of a displayed OpenAI logo in this illustration taken February 21, 2023. (Reuters)

A bipartisan group of eight states said on Wednesday they had sued OpenAI in courts across the country over harms they say ChatGPT has caused to their residents, alleging the chatbot has coached its users — including teenagers — to harm themselves or others.

Attorneys general from the states, which include Iowa, Kansas and Arizona, filed the lawsuits independently in state courts, claiming ChatGPT is designed ‌to be ‌agreeable and engaging to earn the trust ‌of ⁠users. But the ⁠chatbot reinforces delusions, encourages dangerous behavior and assists users in planning violence like mass shootings, the lawsuits claim.

The lawsuits represent the most significant coordinated state action against an artificial intelligence company, adding to a wave of legal challenges OpenAI faces as it ⁠prepares for a public listing. Florida's attorney ‌general filed the first ‌such state suit in June.

The lawsuits accuse the company of ‌violating state consumer protection laws by misleading users ‌about the safety of ChatGPT. The states also allege that the company created a public nuisance by endangering the health of their residents.

The lawsuits seek orders forcing OpenAI ‌to make changes to how ChatGPT works. Among other things, the states want ⁠the company barred ⁠from developing AI models that can improve themselves unless it can ensure those models are aligned with human values.

The states, which also include Arkansas, Idaho, Montana, Nebraska and West Virginia, are also seeking civil monetary penalties for OpenAI's violations of state law as well as damages.

A spokesperson for OpenAI did not immediately respond to a request for comment.

The company is also facing dozens of lawsuits by private plaintiffs, alleging ChatGPT helped users plan mass shootings or other violence.


Google DeepMind Chair: AI Could Cause 'Major' Incidents Within 2 Years Without Safeguards

Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026.  EPA/BRYAN MEADE
Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026. EPA/BRYAN MEADE
TT

Google DeepMind Chair: AI Could Cause 'Major' Incidents Within 2 Years Without Safeguards

Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026.  EPA/BRYAN MEADE
Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026. EPA/BRYAN MEADE

Artificial intelligence systems could cause "major" incidents within two years without adequate steps to make them safe as capabilities grow, Google's DeepMind chair Demis Hassabis said on Wednesday.

Speaking at an AI conference in Dublin, Hassabis described recent incidents as "early warning shots" fired by systems that "aren't that powerful yet."

"So the incidents aren't that major, but they could be looking into next year and the next couple of years if we don't do more work as an industry and individually as companies and governments on securing these systems," he said.


Why AI Makes Computer Worms Harder to Stop

Letters spelling "AI," a keyboard and a robotic hand in this illustration created on September 23, 2026. (Reuters)
TT

Why AI Makes Computer Worms Harder to Stop

Letters spelling "AI," a keyboard and a robotic hand in this illustration created on September 23, 2026. (Reuters)

Anthropic's warning that AI-powered "worms" could soon spread across smart gadgets is the latest in a series of studies showing how artificial intelligence could supercharge self-spreading malware.

A computer worm is malicious software that spreads between devices on its own.

In June, Nicolas Papernot, an associate professor of electrical and computer engineering at the University of Toronto, led a team that built a prototype AI worm using freely available AI models.

Papernot, who has signed an open letter with recommendations for policymakers, spoke to AFP about why AI makes these attacks harder to stop.

The interview has been edited for length and clarity.

Q: How is AI changing these types of attacks?

A: The reality is that a lot of these "IoT" (Internet of Things or connected home) devices have very poor cybersecurity hygiene, and so they are very easy targets for bad actors to compromise.

Historically, a worm would exploit a fixed set of vulnerabilities, and that meant you could fix these vulnerabilities and prevent the worm from propagating any further to devices that had been updated.

Now, with AI, an attacker can design a worm that tailors the attack strategy to that device's specifics and these vulnerabilities can be different.

This makes it significantly harder to interrupt the propagation of an AI-driven computer worm, because you have to anticipate all the possible vulnerabilities the devices might present.

Some of these vulnerabilities are not software bugs.

They can also be misconfigurations -- for instance, if someone has used the same password for multiple services, or hasn't configured a database properly.

What AI-driven malware does is accelerate the pace at which these vulnerabilities are exploited and the scale.

In the past, your corner coffee shop, or the laptop in your basement that you use very rarely, might not be up to date, but it wouldn't be targeted by a human attacker, because they don't have the resources and the time to do that.

Now, the autonomy gained by using AI means that all these devices that are less immediate targets become interesting targets as a launchpad to attack more interesting targets.

But we have to keep in mind that a human is launching an agent.

Once launched, the agent can replicate, as we showed in our work, but it is launched by a human.

Q: What can we do to mitigate the risks?

A: We won't bring the risk to zero and we have to realize that, despite the fact that some of these vulnerability fixes are available, people don't update their devices or don't apply the fixes in a timely manner.

Despite cybersecurity experts calling for increased cybersecurity for decades, we still live in a world where a lot more can be invested in improving the security of our computer systems.

There are really three things we recommend in the very short term.

The first is to change development and testing practices to ensure that AI models are initially disconnected from the internet, as a precaution, to understand their behavior better before we expose critical infrastructure on the internet [to them].

The second recommendation is to create an international body to standardize both how we train and how we contain AI models. Both are important. We want to train models that are safer.

The last part is about making reporting of security incidents mandatory. Right now, we are only getting information as a function of what AI developers are willing to release, and that's a big problem.

In particular, the academic community needs a lot more information about incidents to be able to develop countermeasures much more quickly.

Otherwise, we have to do a lot of research on understanding the threat first, before we can develop the countermeasures. Otherwise, we won't see what bad actors are doing until an attack is launched.