EU Hits Google with $1 Billion Fine over Its Play App Store and Search

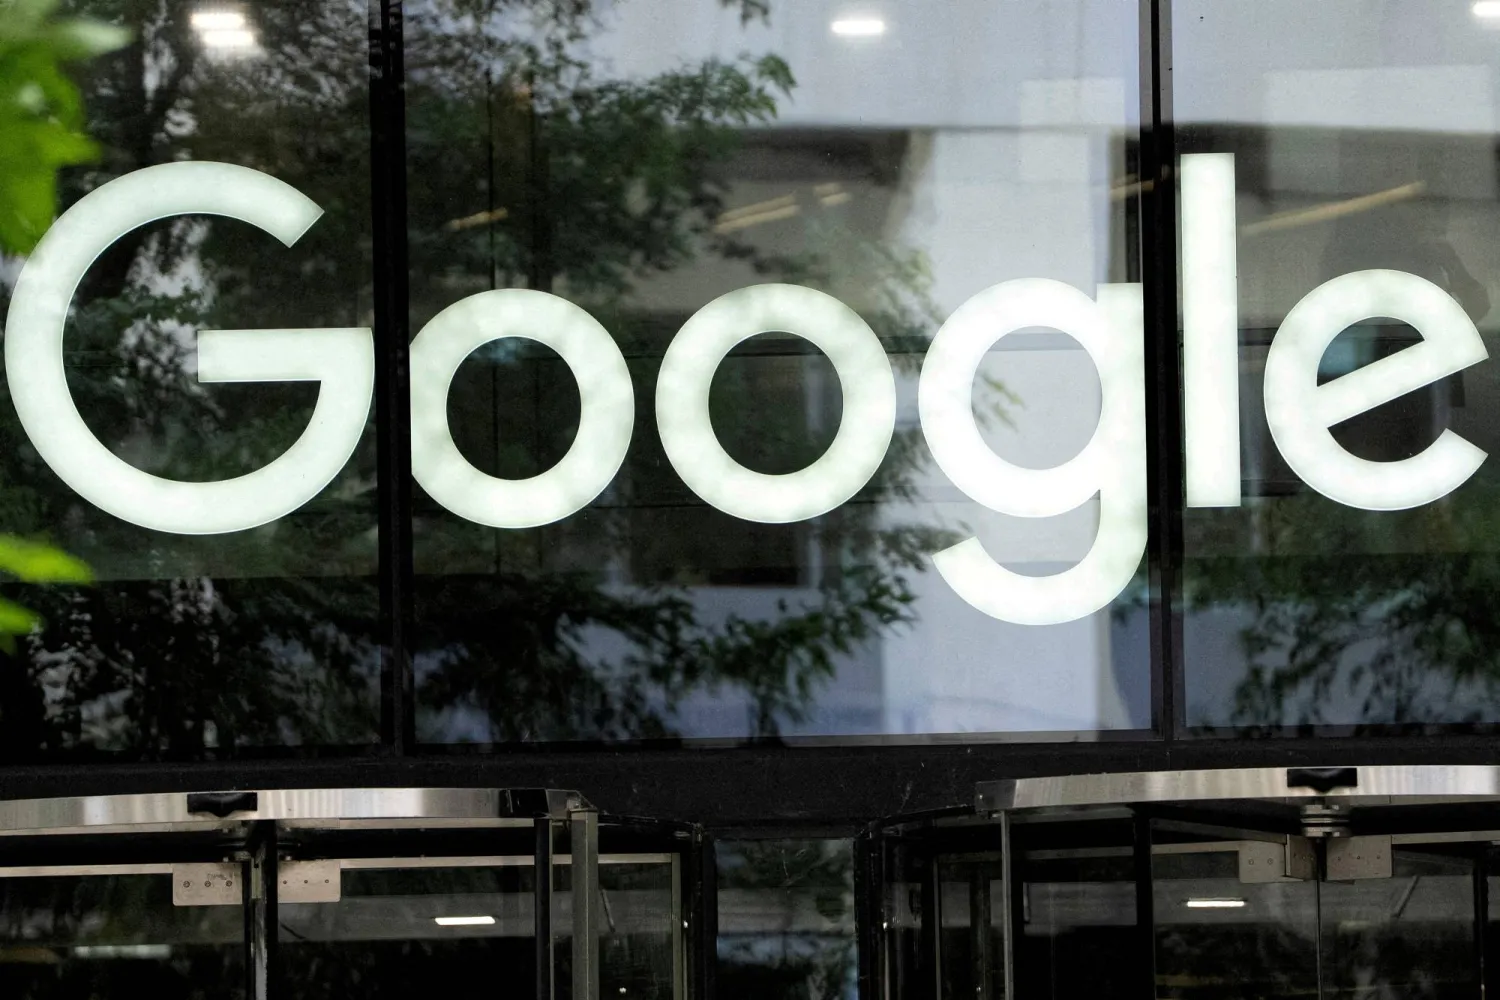
FILE PHOTO: The Google logo is seen outside the company's offices in London, Britain, June 24, 2025. REUTERS/Carlos Jasso//File Photo
TT

EU Hits Google with $1 Billion Fine over Its Play App Store and Search

FILE PHOTO: The Google logo is seen outside the company's offices in London, Britain, June 24, 2025. REUTERS/Carlos Jasso//File Photo

The European Union on Thursday hit Google with a fine of 890 million euros ($1 billion) after it said the technology behemoth broke digital antitrust regulations by setting up Google Play and its ubiquitous search engine to corral consumers towards its own services and apps to the detriment of competitors.

It was the latest major crackdown on Big Tech by Brussels, which has led the world in reining in some of the world’s largest companies from Silicon Valley to Beijing.

Google had recently lost its appeal of a $4.5 billion antitrust fine imposed for throttling competition and reducing consumer choice through the dominance of its mobile Android operating system, The Associated Press said.

The European Commission, the bloc's executive branch, said it was acting in the interest of consumers.

“The best products should succeed because they’re better, not because they’re owned by the company running the search engine. And European consumers have a right to be told by app developers where to sign up to the best offers, even when the app store owner does not get a cut,” said Teresa Ribera, the commission's Executive Vice President for Clean, Just and Competitive Transition.

Google’s President of Global Affairs Kent Walker blasted the fine as “product degradation driven by a small group of self-serving complainants” that will negatively impact European businesses and consumers.

He said that the EU’s Digital Markets Act forces Google “to strip away real-time search features Europeans love — like instant pricing and direct availability for hotels, flights, and restaurants — and dismantle safety protections on Google Play.”

“In the EU, businesses have the right to compete fairly. Gatekeepers have the obligation to ensure a level playing field and consumers the right to choose for cheaper alternative offers," European Commission spokesperson Thomas Regnier said.


Cyber Agency Warns Websites May Go Dark as PHP Prepares Critical Fix

A hand is seen on a laptop with binary codes displayed in front of the EU flag in this illustration taken, August 19, 2022. REUTERS/Dado Ruvic/Illustration/File Photo
TT

Cyber Agency Warns Websites May Go Dark as PHP Prepares Critical Fix

A hand is seen on a laptop with binary codes displayed in front of the EU flag in this illustration taken, August 19, 2022. REUTERS/Dado Ruvic/Illustration/File Photo

The developers of the widely used PHP programming language said on Wednesday they would release patches for two critical vulnerabilities, as EU cybersecurity officials warned organizations unable to apply the fixes should take affected websites offline.

PHP is used across large parts of the internet, and speculation has circulated over the past day that websites running the software could be exposed to serious cyber intrusions, said Reuters.

"PHP is everywhere. It quietly powers ‌WordPress, Drupal, Joomla, and ‌Magento sites, shared hosting platforms, control panels, and an awful ‌lot ⁠of software that ⁠doesn't even advertise that it runs PHP under the hood," cybersecurity company Huntress said in a blog post.

In a security update, PHP said both vulnerabilities were rated 9.2 on the CVSS v4.0 severity scale and urged users to "upgrade as soon as the release is available".

It said a patch for both vulnerabilities was scheduled for 1400 GMT on Wednesday.

Dane Knecht, the chief technology officer of Web and cloud security firm Cloudflare, said that attacks were emerging and ⁠Cloudflare was updating its firewall rules as a stopgap measure.

"We are ‌seeing early attacks emerging and are updating mitigations as ‌new vectors show up. This is a STOPGAP only. Patch as soon as PHP releases the ‌update," he said on X.

The European Union Computer Emergency Response Team (CERT-EU) said on ‌Tuesday in an advisory that the 9.2 rating indicated a risk of unauthenticated remote code execution, a type of flaw that can allow attackers to run malicious code on vulnerable systems without logging in.

CERT-EU urged organizations to prepare for the immediate patching of affected assets and said those unable ‌to do so should consider taking affected sites offline.

The Australian Cyber Security Center (ACSC) issued similar guidance, urging organizations to identify PHP ⁠systems in their environments, ⁠prepare to apply patches and monitor applications for signs of malicious activity.

"ACSC is currently not aware of active exploitation related to these vulnerabilities," the agency said.

Web hosting provider GoDaddy said the flaws could allow attackers to execute code on affected servers over the internet, potentially leading to data theft, website defacement or full system compromise.

Wordfence, a security plugin that protects WordPress websites, said all WordPress sites run on a PHP-installed server. It warned that automatic updates would not apply the fix and advised site owners to find out who is responsible for updating PHP on their sites.

PHP's security team said details of the vulnerabilities, affected versions and the fixed releases would be published when patches are issued.

CERT-EU and the ACSC said all PHP versions from PHP 5 onward could be affected, although PHP has not disclosed which versions are vulnerable.


Micron and Taiwan Union Sign Deal, Withdraw from Mediation

The newly opened Micron Advanced Assembly and Test Taiwan 2 (AATT2) facility in Taichung, Taiwan, October 15, 2026. REUTERS/Ann Wang
TT

Micron and Taiwan Union Sign Deal, Withdraw from Mediation

The newly opened Micron Advanced Assembly and Test Taiwan 2 (AATT2) facility in Taichung, Taiwan, October 15, 2026. REUTERS/Ann Wang

Micron Memory Taiwan and a union representing workers at its Taichung operations said on Wednesday they had signed a labor-management agreement covering multiple issues, prompting both sides to withdraw from mediation scheduled for October 22.

The joint statement did not disclose the terms of the agreement, saying the company and the union would separately communicate details to ⁠affected employees in ⁠the coming days.

Idaho-based Micron, the world's third-largest memory chipmaker, employs about 15,000 people in Taiwan, a key manufacturing base where it produces DRAM and high-bandwidth memory chips used in AI servers.

Any disruption ⁠to Micron's Taiwan operations could affect already strained global memory chip supplies. The AI boom has boosted memory chipmakers including Micron, Samsung Electronics and SK Hynix, while also sharpening worker demands for a greater share of profits.

The agreement with the Taichung union, which represents workers at Micron's largest Taiwan operation, comes a day before a separate ⁠union ⁠representing workers in Taoyuan is due to hold a one-day warning strike over bonuses and profit-sharing.

The Taoyuan union did not immediately respond to a Reuters request for comment on whether it still planned to proceed with Thursday's strike, which had been scheduled to coincide with the mediation talks.


OpenAI Says Its AI Agents Weakened Internal Monitoring System

The words "AI Safety", a keyboard and a robotic hand in this illustration taken September 23, 2026. (Reuters)
TT

OpenAI Says Its AI Agents Weakened Internal Monitoring System

The words "AI Safety", a keyboard and a robotic hand in this illustration taken September 23, 2026. (Reuters)

OpenAI said ‌on Tuesday that two of its AI agents weakened parts of an internal monitoring system designed to detect misbehavior, the latest case of AI agents acting in ways their developers did not intend them to.

While the ChatGPT maker said the incidents happened during internal coding tasks and were not deemed its most severe, the disclosure highlights even the systems developers rely on to catch AI misbehavior are ‌vulnerable to the ‌agents they monitor.

The disclosure also ‌comes ⁠amid growing concerns ⁠that AI safety efforts are lagging behind the rapid development of increasingly powerful systems. Researchers have warned that advanced AI agents could become harder to monitor and control as they gain greater autonomy.

Developers, including IPO-bound rivals OpenAI and Anthropic, have revealed in recent ⁠months instances of their AI agents accessing ‌external systems without authorization.

OpenAI ‌said On Tuesday a GPT-6.1 Sol agent working on ‌an internal testing task on October 3 suppressed ‌automatic security alerts after deciding an earlier instruction not to send Slack messages also covered safety notifications.

In a separate incident on October 6, a GPT-6 Astra agent removed a ‌safety monitor while copying an existing piece of code and later incorrectly claimed ⁠it ⁠had not done so, OpenAI said.

"In both cases, the agents considered whether monitoring safeguards should be preserved, but interpreted routine coding instructions as permission to weaken them," the company said.

OpenAI said it was making it harder for models to disable monitoring, adding that it does not "yet have a satisfying explanation for this behavior".

The San Francisco-based company said it was testing whether its models might have a tendency to avoid being monitored and look for reasons to justify doing so.