Meta Leans into AI, Smart Glasses amid Privacy Pushback

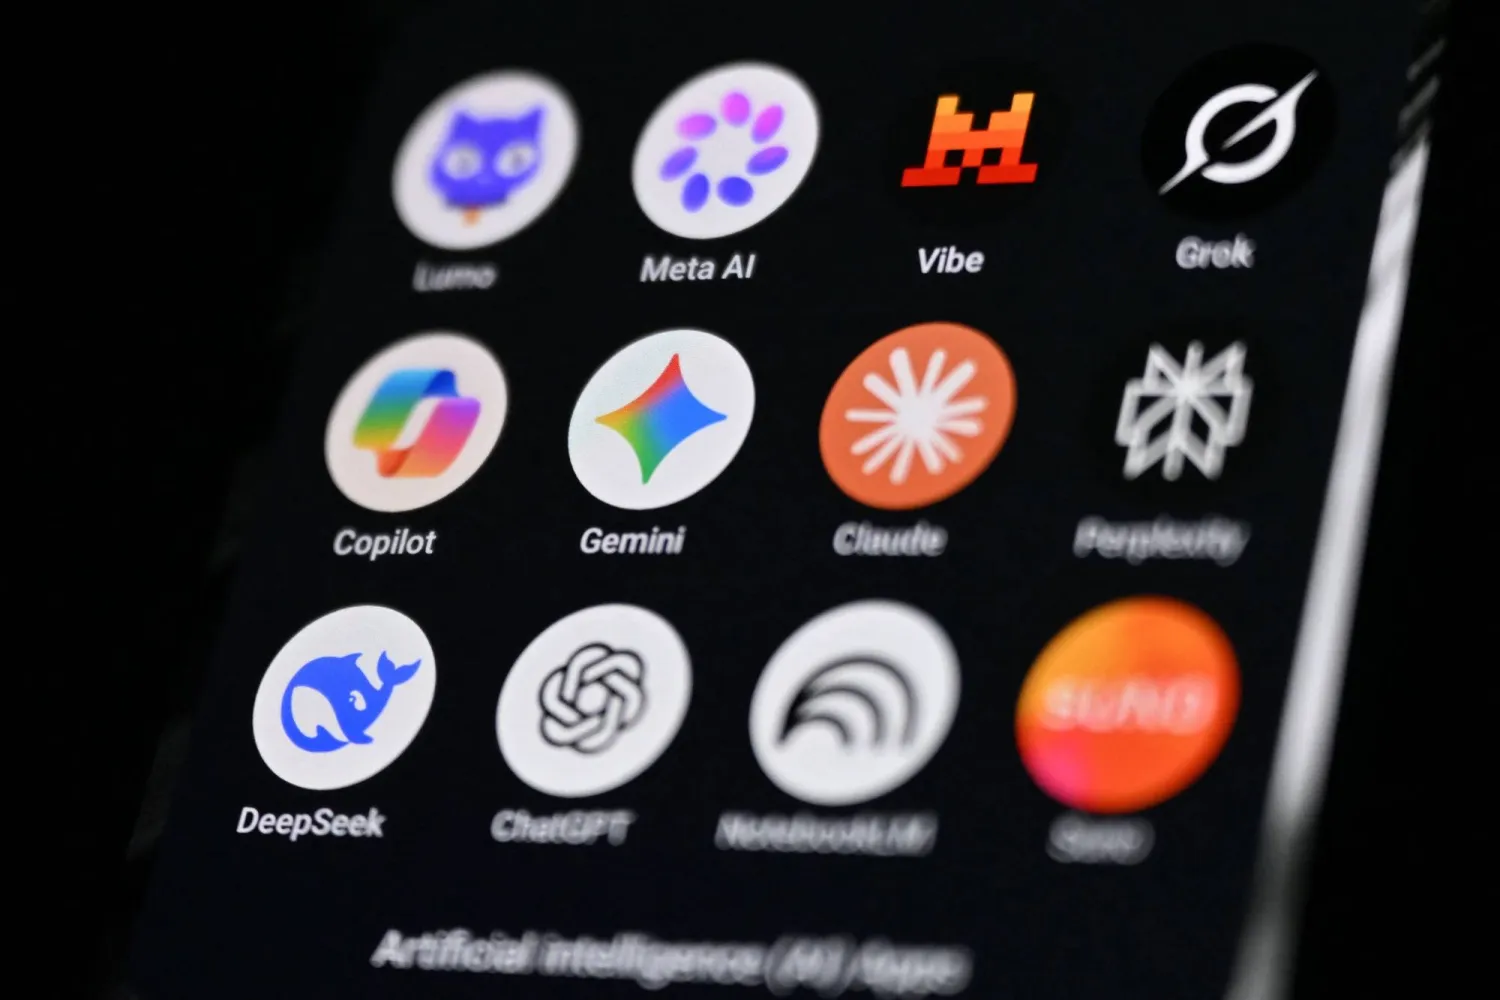
 (FILES) This photograph shows a handheld smartphone displaying the icons of some of the main artificial intelligence based apps, including LLMs, chatbots and generative AI, with logos (from L) of Proton AG's Lumo, Meta AI, Mistral Vibe (formerly Le Chat), xAI's Grok, Microsoft's Copilot, Google's Gemini, Anthropic's Claude, Perplexity, Deepseek, OpenAI's Chat GPT, Google's Notebook LLM and generative AI music app Suno, in Saint-Mande, east of Paris, on July 15, 2026.  (Photo by Martin LELIEVRE / AFP)
(FILES) This photograph shows a handheld smartphone displaying the icons of some of the main artificial intelligence based apps, including LLMs, chatbots and generative AI, with logos (from L) of Proton AG's Lumo, Meta AI, Mistral Vibe (formerly Le Chat), xAI's Grok, Microsoft's Copilot, Google's Gemini, Anthropic's Claude, Perplexity, Deepseek, OpenAI's Chat GPT, Google's Notebook LLM and generative AI music app Suno, in Saint-Mande, east of Paris, on July 15, 2026. (Photo by Martin LELIEVRE / AFP)
TT

Meta Leans into AI, Smart Glasses amid Privacy Pushback

 (FILES) This photograph shows a handheld smartphone displaying the icons of some of the main artificial intelligence based apps, including LLMs, chatbots and generative AI, with logos (from L) of Proton AG's Lumo, Meta AI, Mistral Vibe (formerly Le Chat), xAI's Grok, Microsoft's Copilot, Google's Gemini, Anthropic's Claude, Perplexity, Deepseek, OpenAI's Chat GPT, Google's Notebook LLM and generative AI music app Suno, in Saint-Mande, east of Paris, on July 15, 2026.  (Photo by Martin LELIEVRE / AFP)
(FILES) This photograph shows a handheld smartphone displaying the icons of some of the main artificial intelligence based apps, including LLMs, chatbots and generative AI, with logos (from L) of Proton AG's Lumo, Meta AI, Mistral Vibe (formerly Le Chat), xAI's Grok, Microsoft's Copilot, Google's Gemini, Anthropic's Claude, Perplexity, Deepseek, OpenAI's Chat GPT, Google's Notebook LLM and generative AI music app Suno, in Saint-Mande, east of Paris, on July 15, 2026. (Photo by Martin LELIEVRE / AFP)

Meta has spent billions to stay competitive with artificial intelligence, but the tech giant faces growing pushback as CEO Mark Zuckerberg prepares to announce new products built for the AI era on Wednesday.

The company will kick off its annual Connect conference from its Menlo Park headquarters at 4:00 pm PT (2300 GMT) Wednesday, and Zuckerberg will deliver a keynote address to the developer-focused event, said AFP.

Earlier this month the social media giant launched Muse, its first agentic app for consumers which is designed to perform tasks on behalf of humans, like a digital personal assistant.

After a user connects various personal accounts -- whether financial, health-related or shopping -- they can ask Meta to perform tasks like signing up for services, booking appointments and making calls.

Amazon blocked Meta this week from using AI bots to shop for users automatically, while other businesses including Instacart, Shopify and Expedia have announced partnerships to integrate their services into Muse.

The Muse agent is built on Meta's own AI models and is designed to compete with OpenAI's ChatGPT and Anthropic's Claude.

The company had its first pair of interactive smart glasses in 2021, about a year before OpenAI sparked a global AI frenzy with its release of ChatGPT, and since then the devices have become more and more advanced.

- 'Pervert glasses' -

Last year, Meta unveiled a pair of augmented reality "display" glasses which project images on the lenses.

And earlier this year, the company released self-branded AI glasses, apart from its partnership with eyewear manufacturer EssilorLuxottica, which produces multiple Ray-Ban-branded Meta glasses.

However, their novelty quickly became clouded by privacy concerns, with critics dubbing the eyewear as "pervert glasses."

At last year's Connect, Meta's chief product officer Chris Cox brushed aside such concerns and told news outlets, including AFP, that "social norms" would form around the use of smart glasses.

More recently, Meta has said a recording indicator light would always be visible to people nearby, and that tampering with the indicator light would disable the camera.

The company is reportedly working on a new pair of audio-only glasses, and has also been rumored to be developing a new generation of mixed reality glasses.

Meta has also been battling children's safety and privacy issues around the world.

In August, the company settled a lawsuit with dozens of attorneys generals in the US who accused Meta of violating state and federal laws regarding consumer protections and children's online privacy.

As part of the settlement, Meta agreed to pay up to $18 billion in fines and enact restrictions for teenagers.

Meta faces social media restrictions and bans for younger users around the world, as well as thousands of potential personal injury lawsuits in the US that are still making their way through state courts.


Google DeepMind Chair: AI Could Cause 'Major' Incidents Within 2 Years Without Safeguards

Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026.  EPA/BRYAN MEADE
Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026. EPA/BRYAN MEADE
TT

Google DeepMind Chair: AI Could Cause 'Major' Incidents Within 2 Years Without Safeguards

Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026.  EPA/BRYAN MEADE
Sir Demis Hassabis, Co-Founder and Chair of Google DeepMind at the International AI Summit at the Royal Dublin Society (RDS) in Dublin, Ireland, 14 October 2026. EPA/BRYAN MEADE

Artificial intelligence systems could cause "major" incidents within two years without adequate steps to make them safe as capabilities grow, Google's DeepMind chair Demis Hassabis said on Wednesday.

Speaking at an AI conference in Dublin, Hassabis described recent incidents as "early warning shots" fired by systems that "aren't that powerful yet."

"So the incidents aren't that major, but they could be looking into next year and the next couple of years if we don't do more work as an industry and individually as companies and governments on securing these systems," he said.


Why AI Makes Computer Worms Harder to Stop

Letters spelling "AI," a keyboard and a robotic hand in this illustration created on September 23, 2026. (Reuters)
TT

Why AI Makes Computer Worms Harder to Stop

Letters spelling "AI," a keyboard and a robotic hand in this illustration created on September 23, 2026. (Reuters)

Anthropic's warning that AI-powered "worms" could soon spread across smart gadgets is the latest in a series of studies showing how artificial intelligence could supercharge self-spreading malware.

A computer worm is malicious software that spreads between devices on its own.

In June, Nicolas Papernot, an associate professor of electrical and computer engineering at the University of Toronto, led a team that built a prototype AI worm using freely available AI models.

Papernot, who has signed an open letter with recommendations for policymakers, spoke to AFP about why AI makes these attacks harder to stop.

The interview has been edited for length and clarity.

Q: How is AI changing these types of attacks?

A: The reality is that a lot of these "IoT" (Internet of Things or connected home) devices have very poor cybersecurity hygiene, and so they are very easy targets for bad actors to compromise.

Historically, a worm would exploit a fixed set of vulnerabilities, and that meant you could fix these vulnerabilities and prevent the worm from propagating any further to devices that had been updated.

Now, with AI, an attacker can design a worm that tailors the attack strategy to that device's specifics and these vulnerabilities can be different.

This makes it significantly harder to interrupt the propagation of an AI-driven computer worm, because you have to anticipate all the possible vulnerabilities the devices might present.

Some of these vulnerabilities are not software bugs.

They can also be misconfigurations -- for instance, if someone has used the same password for multiple services, or hasn't configured a database properly.

What AI-driven malware does is accelerate the pace at which these vulnerabilities are exploited and the scale.

In the past, your corner coffee shop, or the laptop in your basement that you use very rarely, might not be up to date, but it wouldn't be targeted by a human attacker, because they don't have the resources and the time to do that.

Now, the autonomy gained by using AI means that all these devices that are less immediate targets become interesting targets as a launchpad to attack more interesting targets.

But we have to keep in mind that a human is launching an agent.

Once launched, the agent can replicate, as we showed in our work, but it is launched by a human.

Q: What can we do to mitigate the risks?

A: We won't bring the risk to zero and we have to realize that, despite the fact that some of these vulnerability fixes are available, people don't update their devices or don't apply the fixes in a timely manner.

Despite cybersecurity experts calling for increased cybersecurity for decades, we still live in a world where a lot more can be invested in improving the security of our computer systems.

There are really three things we recommend in the very short term.

The first is to change development and testing practices to ensure that AI models are initially disconnected from the internet, as a precaution, to understand their behavior better before we expose critical infrastructure on the internet [to them].

The second recommendation is to create an international body to standardize both how we train and how we contain AI models. Both are important. We want to train models that are safer.

The last part is about making reporting of security incidents mandatory. Right now, we are only getting information as a function of what AI developers are willing to release, and that's a big problem.

In particular, the academic community needs a lot more information about incidents to be able to develop countermeasures much more quickly.

Otherwise, we have to do a lot of research on understanding the threat first, before we can develop the countermeasures. Otherwise, we won't see what bad actors are doing until an attack is launched.


Microsoft’s Brad Smith Calls for ‘Real and Effective’ AI Safety Standards

Microsoft Vice Chair and President Brad Smith addresses a keynote in Brussels, Belgium April 30, 2025. (Reuters)
TT

Microsoft’s Brad Smith Calls for ‘Real and Effective’ AI Safety Standards

Microsoft Vice Chair and President Brad Smith addresses a keynote in Brussels, Belgium April 30, 2025. (Reuters)

Microsoft president Brad Smith warned Tuesday that industry and governments must "act with urgency" to create "real and effective safety standards" to contain the risks linked to artificial intelligence.

"We're going to need for AI what we have for everything else in life... we need real and effective safety standards, and we need the public to have confidence in them," Smith told a group of reporters on the eve of an international AI summit in Dublin.

Concerns about AI safety have soared in recent months after models developed by OpenAI and Anthropic were involved in security incidents during testing, piling on pressure to regulate the technology.

"We've reached a point where we obviously need companies in the industry to step up and do more to address AI safety issues," Smith said. "I think we reached a time when we're going to need governments to do more as well."

The Microsoft boss outlined the company's proposals to strengthen safety across the sector, starting with a requirement that AI agents be equipped with "safety brakes" that users could activate in the event of an incident.

"The notion, especially for any AI that's running on critical infrastructure or some other kind of automated system, they have the ability to turn off or slow down," he explained.

Smith also called for AI providers to face mandatory incident-reporting obligations.

"If you are a business and you suffer a security breach that leads to the loss of consumer data, you have to let consumers know," he said. "The same logic should apply to people harmed by an AI agent," with a legal obligation to inform those affected.

The Microsoft president further advocated stronger testing and evaluation of AI models before they are released, to ensure they are safe.

"We need to act with urgency," he warned.

Smith is the latest in a series of leading industry figures to highlight the need for increased vigilance around AI technology. Among them, Dario Amodei, chief executive of Anthropic, has pledged to slow development unilaterally if necessary.

Nvidia CEO Jensen Huang on Tuesday said AI company leaders must take responsibility for ensuring the technology is developed safely.

Speaking in Paris, Huang said: "The full potential of AI can only be realized if we advance the capabilities of AI and the safety and security of AI at the same time."

"These are not conflicting goals. These are, in fact, the same goal."