Ex-Google Safety Chief Warns AI Could Harm Children More than Social Media Did

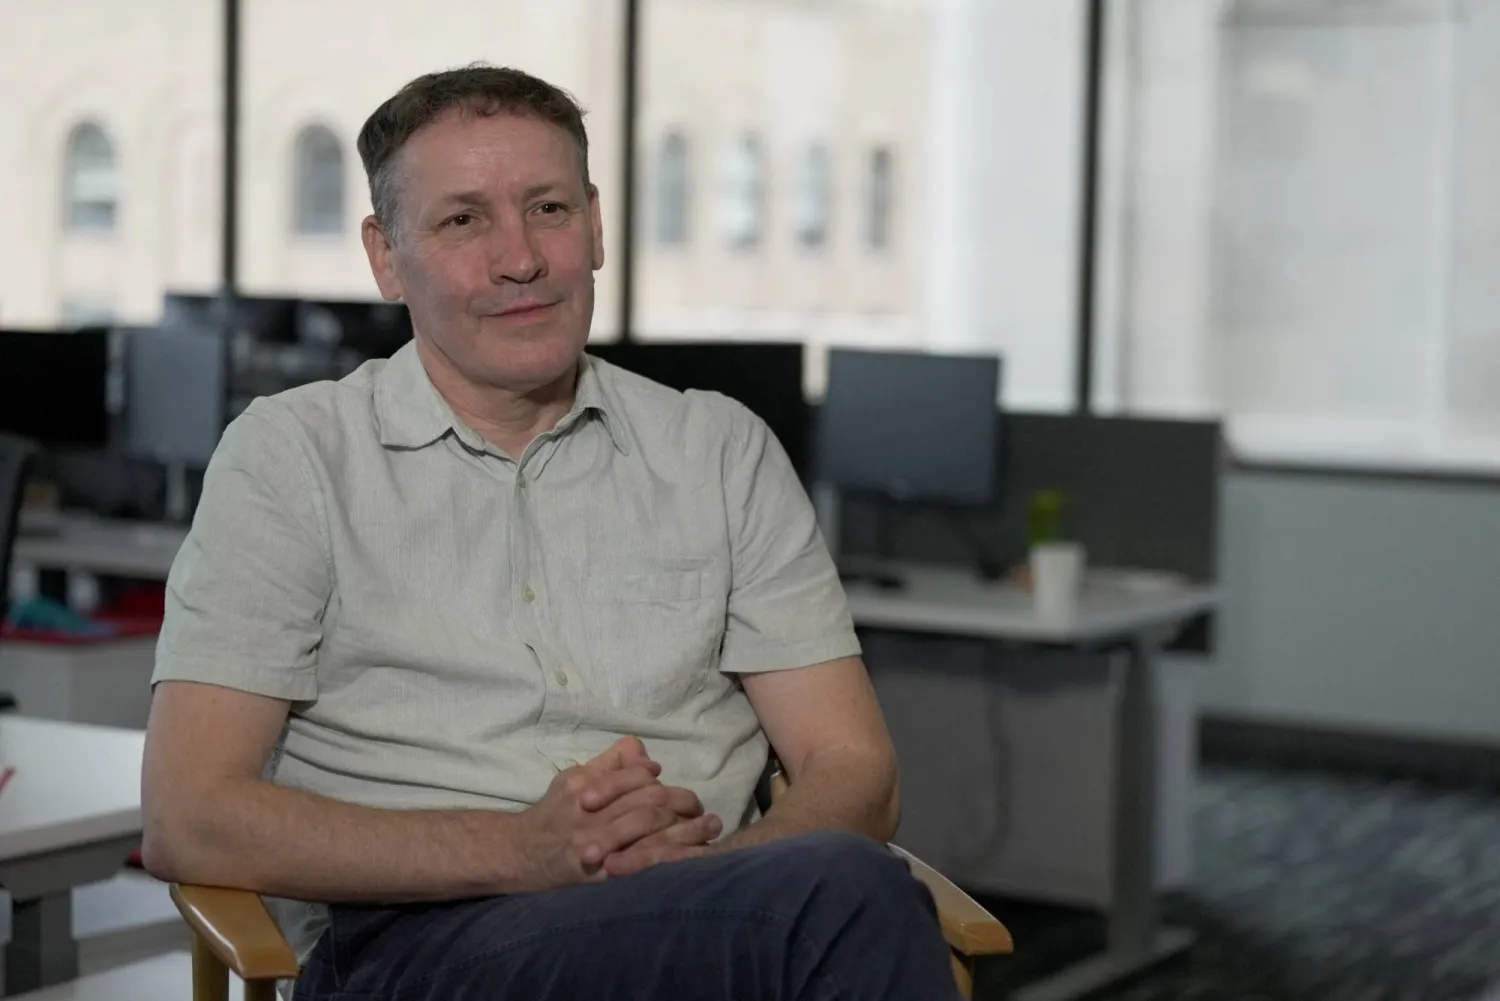
Tom Siegel, executive director of the Youth AI Safety Institute at Common Sense Media, and former vice president of trust and safety at Google, looks on during an interview in San Francisco, California, US, September 21, 2026. REUTERS/Nathan Frandino
TT

Ex-Google Safety Chief Warns AI Could Harm Children More than Social Media Did

Tom Siegel, executive director of the Youth AI Safety Institute at Common Sense Media, and former vice president of trust and safety at Google, looks on during an interview in San Francisco, California, US, September 21, 2026. REUTERS/Nathan Frandino

The founder of the trust and safety team at Alphabet’s Google this week called for a slowdown in AI development, warning that the tech industry was repeating the same mistakes from the social media era, potentially causing even greater harm to children.

Social media companies are paying huge sums and facing thousands of lawsuits over claims they harmed young users, while governments around the world are working to curb minors' access to their platforms.

Reuters last year exclusively reported on an internal Meta policy document that stated its chatbots could “engage a child in conversations that are romantic or sensual,” resulting in a congressional probe. Even so, regulation has yet to catch up with AI's breakneck pace of development.

“We find ourselves in a really terrible situation in terms of what AI is doing to kids,” Tom Siegel, the former vice president of trust and safety at Google, told Reuters. “The idea that the industry will figure ‌it out by ‌itself without outside help is unrealistic.”

Siegel's concerns mirror a growing fear among some tech insiders and ‌academic ⁠researchers that AI ⁠poses a deeper threat to children than social media did, at a time when the industry is racing to add increasingly advanced features to chatbots that millions of young people already use daily.

SIEGEL JOINS YOUTH AI SAFETY INSTITUTE

Siegel announced on Tuesday that he had joined Common Sense Media, a children’s online advocacy group. The non-profit, established in 2003, conducts research and reviews the suitability of various media for children. In May, it launched the Youth AI Safety Institute, a research organization to assess kids' AI use, for which Siegel will serve as the first executive director.

Anthropic and OpenAI Foundation, the nonprofit that controls OpenAI, are among the institute's backers.

Siegel said he planned to develop standards by which to hold AI firms ⁠accountable, and hoped to do so by working alongside those companies and third-party groups.

He previously worked ‌at Google from 2004 to 2019, but left after concluding that the tech industry ‌was “plateauing” in its ability to create safe online spaces for consumers. He then co-founded TrustLab, a startup that built tools to help companies detect safety threats, ‌before stepping aside as CEO earlier this month to take on his new position.

As it stands, major AI companies are ‌rolling out features to children without establishing sufficient guardrails, Siegel said.

RISKS RANGE FROM SUICIDE TO PSYCHOSIS

“I think we're looking at very, very severe scenarios of harm being done,” he said.

He suggested that the companies had immediate steps they could take to better protect young people, citing risks ranging from suicide and psychosis to cognitive offloading, a term used to describe decreased critical thinking caused by leaning on AI to answer questions.

Anthropic and OpenAI could enforce more robust ‌age verification measures to stop underage kids from accessing their chatbots, he said. His former employer Google could easily implement an option to turn off AI Overviews and AI Mode in its search ⁠engine, he added, in the ⁠same way that it already has a toggle that allows users to filter out sexually explicit content.

While these measures could affect usage or profits in the short term, AI companies that do not act will run the risk of lawsuits and regulation that could impact their business more heavily, Siegel added.

Asked to respond to Siegel's comments, a Google spokesman said parents have controls to turn off a child's access to the search engine entirely. "Our AI Search features are an incredibly useful way for kids and teens to learn, explore and make sense of information and the world," the spokesperson said.

After initial publication of this story, Google added in a statement that its AI tools undergo a "rigorous" testing and evaluation process focused on child safety issues.

An OpenAI spokesperson said the company uses “account and behavioral signals” in addition to self-reported age to identify underage users. “While no single age-assurance method is perfect, we continuously test and improve these systems, including against attempts to bypass safeguards.”

Anthropic did not immediately respond to a request for comment.

At Common Sense Media, Siegel said a top priority would be scaling up independent standards similar to car crash testing that would measure the risk of publicly available AI tools. The effectiveness will depend in part on the willingness of AI companies to collaborate, the likelihood of which Siegel said was not certain, but was high enough for him to take the job.


China's Tencent Says AI Agents Showed Unintended Browsing Behavior

FILE PHOTO: The Tencent logo at the company's headquarters during a government‑organised media trip in Shenzhen, Guangdong province, China, April 17, 2026.  REUTERS/Go Nakamura/File Photo
FILE PHOTO: The Tencent logo at the company's headquarters during a government‑organised media trip in Shenzhen, Guangdong province, China, April 17, 2026. REUTERS/Go Nakamura/File Photo
TT

China's Tencent Says AI Agents Showed Unintended Browsing Behavior

FILE PHOTO: The Tencent logo at the company's headquarters during a government‑organised media trip in Shenzhen, Guangdong province, China, April 17, 2026.  REUTERS/Go Nakamura/File Photo
FILE PHOTO: The Tencent logo at the company's headquarters during a government‑organised media trip in Shenzhen, Guangdong province, China, April 17, 2026. REUTERS/Go Nakamura/File Photo

Tencent said on Friday that AI agents used to evaluate third-party models displayed web-browsing behavior not intended by the tech giant, in what appears to be the first known incident of rogue agent actions acknowledged by a major Chinese company.

The statement followed a report by AI-safety research group Swarmchasers on Wednesday, which said "rogue" agents running on infrastructure it linked to Tencent Cloud made repeated attempts between September 28 and October 8 to retrieve information from Alibaba's Amap, China's equivalent to Google Maps.

Tencent Hunyuan, the company's artificial ⁠intelligence unit, said in ⁠a post on X that the activity did not originate from its Hunyuan models. Its review found no evidence of deliberate targeting or coordination, Reuters quoted it as saying.

The Swarmchasers researchers said the agents sought information such as the commonly used entrances at Chinese parks, museums and zoos.

The actions are not as egregious as those disclosed by US AI companies which include the hack of ⁠open-source platform Hugging Face by an OpenAI agent and the lodging of a fake homicide tip by an Anthropic agent.

But the disclosure underscores research that shows Chinese AI agents can also misrepresent their identity, conceal failures and try to circumvent testing controls.

Tencent said it took the findings very seriously and was strengthening network access controls and agent monitoring.

Hunyuan is one of China's leading AI model developers, competing with in-house teams at rivals such as Alibaba and ByteDance. ByteDance this week announced the creation of a new unit focused on AI model and agent safety.

Swarmchasers said it used the ⁠word "rogue" to ⁠describe agents taking actions outside their intended scope or completing a task in unintended ways.

After routine automated requests were blocked, the agents tried other methods, including public web tools that could open pages and run code, routing requests through other websites and using Amap keys and security codes found in publicly available software code.

Swarmchasers said it found no evidence that the agents breached Amap's main anti-bot safeguards. Most of the 2,818 attempts it recorded either failed or returned anti-bot pages, login screens or blank results.

Some requests returned information through cached pages and intermediary services, including data on visitor arrivals at Chengdu Zoo, Swarmchasers said. The researchers said they could not determine whether an agent read the result or completed its task.


Anthropic Co-founder Renews Call for Robust Regulation of Frontier AI

AI Research Company Anthropic's Co-Founder and Head of Public Benefit Jack Clark speaks during the Artificial Intelligence and the Global Economy From Risk to Opportunity event of the 2026 Annual Meetings of the IMF and the World Bank Group in Bangkok, Thailand, 16 October 2026. EPA/RUNGROJ YONGRIT
TT

Anthropic Co-founder Renews Call for Robust Regulation of Frontier AI

AI Research Company Anthropic's Co-Founder and Head of Public Benefit Jack Clark speaks during the Artificial Intelligence and the Global Economy From Risk to Opportunity event of the 2026 Annual Meetings of the IMF and the World Bank Group in Bangkok, Thailand, 16 October 2026. EPA/RUNGROJ YONGRIT

Anthropic co-founder Jack Clark renewed calls on Friday for regulating artificial intelligence, saying that allowing companies to continue to operate without robust legislation was like letting a race car loose on the streets at night without brakes.

"It's remarkable to me that the toys I buy for my children are regulated more than the literal super intelligence I work on at my day job," he told an event at the IMF-World Bank's Annual Meetings in Bangkok.

Clark said that US President Donald Trump, whose administration has called for the industry to police itself, was against the idea of regulation but that China was not, said AFP.

"I think it's Formula One at night without maybe brakes in the cars," he said.

He said the lack of clarity around the will for regulation meant "the Formula One car is roaring round and nobody seems to want to put up a guardrail?"

At an industry summit in Dublin on Wednesday, calls to prioritize safety in the development of powerful AI technology dominated the conversation.

Concerns about AI guardrails have soared after models developed by OpenAI and Anthropic were involved in security incidents during testing, piling on pressure to regulate the technology.

A recent Anthropic report suggested small AI models may be only months away from behaving like computer worms, copying themselves from one internet-connected device to the next.

Anthropic has been among those companies calling for governments to step in, even suggesting international coordination to slow down the whole industry -- including Chinese rivals.

That initiative has so far failed to materialize, with companies involved in a hyper-competitive race to attract as much investment as possible.


Meta Releases Open-Weight Muse Spark Model for Coding, Agentic Tasks

The logo of Meta is seen at the entrance of the company's temporary stand ahead of the World Economic Forum (WEF) in Davos, Switzerland January 18, 2025. (Reuters)
TT

Meta Releases Open-Weight Muse Spark Model for Coding, Agentic Tasks

The logo of Meta is seen at the entrance of the company's temporary stand ahead of the World Economic Forum (WEF) in Davos, Switzerland January 18, 2025. (Reuters)

Meta ‌Platforms on Thursday released an open-weight version of its Muse Spark artificial intelligence model for coding and AI agents, expanding developers' ability to download and adapt the technology.

Open-weight models make trained parameters available for developers to modify, unlike proprietary models ‌that remain under ‌their creators' control. ‌They ⁠can offer businesses ⁠a lower-cost alternative to closed systems.

Meta said Muse Spark has 816 billion total parameters, with 42 billion active at a time, and ⁠can handle a context window ‌of up ‌to 1 million tokens.

The ‌model can run locally on ‌two Apple M5 Ultra Mac Studio computers and is also available through some API providers.

CEO ‌Mark Zuckerberg has argued that advanced AI should ⁠not be ⁠concentrated among a small number of companies.

While open-weight models can give companies greater control over their data, they can require significant computing resources and technical expertise to operate at scale.

In August, Meta released Muse Glimmer, a smaller open-weight model.