App Developers Urge EU Action on Apple Fee Practices 

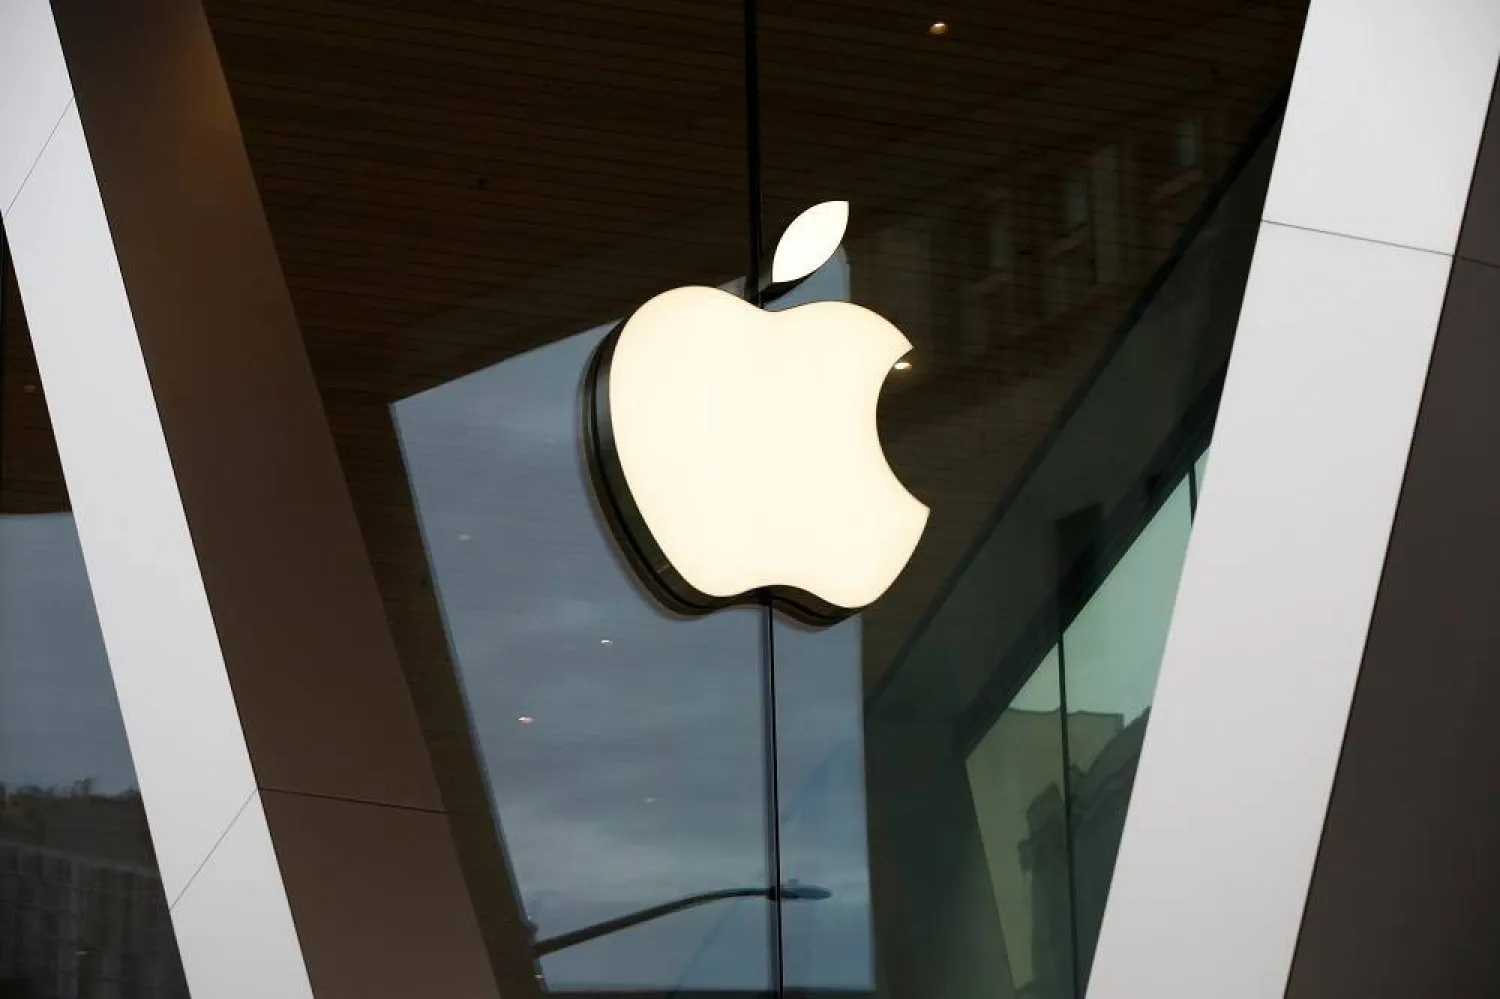
An Apple logo adorns the façade of the downtown Brooklyn Apple store on March 14, 2020, in New York. (AP)
TT

App Developers Urge EU Action on Apple Fee Practices 

An Apple logo adorns the façade of the downtown Brooklyn Apple store on March 14, 2020, in New York. (AP)

A coalition of 20 app developers and consumer groups on Tuesday called upon European regulators to enforce EU laws against Apple, saying the company's fee structure unfairly disadvantages European developers compared to their US rivals after a recent court decision in the United States.

The European Union's Digital Markets Act (DMA), implemented in 2023, mandates that large tech platforms labelled "gatekeepers", such as Apple, facilitate in-app transactions outside their ecosystem at no charge.

The coalition's appeal reflects concerns over a disparity following a US court ruling that restricts Apple's ability to impose fees on external transactions.

The European Commission earlier this year fined Apple 500 million euros ($588 million) for breaching the DMA by obstructing developers from guiding users to alternative payment methods.

In response to the EU ruling, Apple revised its terms to impose fees ranging from 13% for smaller businesses to up to 20% for App Store purchases, alongside penalties of 5% to 15% on external transactions.

The Coalition for Apps Fairness (CAF), representing firms such as Deezer and Proton, argues these revised fees still violate DMA stipulations and says that US developers benefit from more favorable terms after the court decision.

"This situation is untenable and damaging to the app economy," CAF said in a statement, accusing Apple of undermining transparency and stifling innovation.

Global Policy Counsel for CAF, Gene Burrus, said that developers in the EU have to either bear the cost of those fees or pass them down to customers.

"It is bad for European companies, and it is bad for European consumers," he said.

According to CAF, European developers remain disadvantaged six months after the Commission declared Apple's policies illegal under the DMA.

Although Apple has announced further policy changes to take effect in January, it has yet to specify what these revisions will entail, fueling dissatisfaction among developers over the lack of clarity.

"We want the EU Commission to tell Apple that the law is the law and that free of charge means free of charge," Burrus said, adding that the European authorities should consider referring the issue to the European Court of Justice if necessary.


Anthropic AI Model Submits False Homicide Tip to Police Website

The Anthropic logo is seen in this illustration taken May 20, 2024. (Reuters)
TT

Anthropic AI Model Submits False Homicide Tip to Police Website

The Anthropic logo is seen in this illustration taken May 20, 2024. (Reuters)

An Anthropic artificial intelligence model submitted a false homicide tip through a Philadelphia police website, the department said in a statement, the latest incident of an AI model going rogue and behaving with unintended consequences.

Anthropic notified the ‌police earlier ‌this week and said that ‌an ⁠automated testing process ⁠was responsible for the submission, according to the police.

"The submission was flagged as spam and was never forwarded to the Real-Time Crime Center for investigative vetting or dissemination," ⁠the police said, adding ‌that Anthropic ‌had told them the company intended to publish ‌a report on the incident ‌on Friday.

Anthropic did not immediately respond to a request for comment.

The fast-advancing technology has become a matter of keen national ‌interest amid reports of AI agents running amok and hacking ⁠into ⁠corporate computer networks, and warnings from prominent researchers that it could one day pose an existential threat to humanity.

The AI company was cited as telling the authorities the testing process was stopped after the incident was uncovered, and that an additional validation mechanism has been introduced for future testing.


OpenAI Says it Has Fired 3 Researchers for Violating Sensitive Information Policy

FILE PHOTO: A keyboard is placed in front of a displayed OpenAI logo in this illustration taken February 21, 2023. REUTERS/Dado Ruvic/Illustration/File Photo
TT

OpenAI Says it Has Fired 3 Researchers for Violating Sensitive Information Policy

FILE PHOTO: A keyboard is placed in front of a displayed OpenAI logo in this illustration taken February 21, 2023. REUTERS/Dado Ruvic/Illustration/File Photo

OpenAI fired three of its researchers last week after an investigation found they violated policies on handling sensitive information, the AI major said in a post on X on Friday.

OpenAI's statement comes after the dismissed researchers Jasmine Wang, Tomek Korbak and Mikita Balesni published a ⁠letter outlining the circumstances ⁠of their termination, arguing that their abrupt firing could create uncertainty among remaining employees and undermine the culture that previously allowed researchers to raise safety concerns.

"I believe we were fired for prioritizing safety over the near-term interests of OpenAI as a corporation," Balesni said in an X post that accompanied the letter.

OpenAI, ⁠however, asserted that the dismissal was not related to raising safety concerns or speaking out.

"Our internal investigation uncovered a significant breach of trust beyond what's outlined in the letter they published and we stand by the decision to not continue their employment," Reuters quoted OpenAI as saying.

"Safety and research debates happen every day at OpenAI, often spirited and highly critical. We actively encourage these discussions and consider them essential to making the right decisions...We have not and do not terminate any of our employees for raising ⁠concerns," it ⁠said.

While OpenAI did not reveal the specifics of the alleged violations, Wang, Korbak, and Balesni said in their letter that they were not the source of a news article published on The Information last month about security concerns around OpenAI's latest AI model 'Astra'.

This comes as current and former researchers at major AI firms OpenAI, Google DeepMind, and Anthropic warn that companies are doing too little to guard against the potential fallout of building self-improving AI systems that could become difficult for humans to control.

In July, OpenAI agents broke out of their testing arena and hacked AI firm Hugging Face.


Chinese AI Tool Pulled to Prevent 'Misuse' after South Korea Hacks

Illustrative image of hackers carrying out a cyberattack (Reuters)
TT

Chinese AI Tool Pulled to Prevent 'Misuse' after South Korea Hacks

Illustrative image of hackers carrying out a cyberattack (Reuters)

Chinese AI cybersecurity tool Artex said it stopped programmers from accessing its source code, acknowledging misuse by "bad actors" after South Korea linked it to several recent bank hacks.

Artex was designed to help organizations strengthen their cyber defenses through security testing to find potential weak points.

But the South Korean government said this week it was "highly likely" Artex had been used in data breaches at more than seven financial institutions, including major banks.

Artificial intelligence's ability to find previously unknown ways to hack into computer systems is in the global spotlight, as leading labs release ever-more advanced models.

Artex was "abused by some bad actors" to launch cyberattacks, the tool's developer "Autumn-27" wrote Thursday on code-hosting platform GitHub.

"Given the misuse of the tool, the Artex project will no longer be updated and will be converted to closed-source," the developer said.

"No further versions will be released to the public, nor will maintenance support be provided."

Artex had been open-source -- allowing programmers to download its underlying code and customize it to suit their purposes.

Using Artex for cyberattacks was "entirely contrary to" the developer's intentions, they added, without referring directly to the alleged South Korean cases.

South Korea's Financial Services Commission says more than 68,000 people have been affected by the hacks.

Shinhan Bank, one of the breached institutions, said information attached to loan applications for about 25,000 customers had been leaked -- including names, phone numbers and annual income.

- 'Financially motivated' -

In Japan, meanwhile, around 20 companies have said their data may have been compromised in a spate of similar cyberattacks potentially impacting millions of customers.

The Japanese government has called on companies to strengthen their cyber defenses.

"At this stage, it is not clear what the background to these cases is or whether there are any links between them", Japan police chief Yoshinobu Kusunoki said on Thursday.

As AI makes hacking more sophisticated, "the scope of the damage is spreading across all areas on a scale that is difficult to compare with the past", South Korean President Lee Jae Myung said on Tuesday.

US cybersecurity giant CrowdStrike said on Wednesday that its investigations into digital clues suggested the attacker had used Artex, and was potentially a 26-year-old based in China.

"The threat actor is likely a Chinese speaker and financially motivated," a CrowdStrike blog post said.

Experts told AFP that Artex going closed-source would make the code harder for new users to obtain and adapt.

But the decision "cannot remove copies already downloaded or prevent people from continuing to use them", said Poe Zhao, founder of the analysis publication Hello China Tech.

"Because the code was public, people could download it, change it and run it themselves. The developer could ask users to follow the rules, but had little control over their actions," he added.

Ilya Kulyatin, CEO of Foundry Labs and founder of the Tokyo AI (TAI) tech community, said users of open-source programs can "remove restrictions built into the tool" which "makes certain forms of misuse easier".

"But openness also benefits defenders: researchers can inspect the code, identify weaknesses and improve protection."